
New features and enhancements
September 2026
- Consent screen: The consent screen is being removed because access to Unit4 applications and the associated processing of customer data are governed by the contractual relationship between Unit4 and the customer organization. Removing this additional step provides a clearer and more efficient sign-in experience.
- For additional information about Unit4’s approach to data processing, security, and privacy, please refer to the Unit4 Security and Privacy webpage and the Unit4 Legal Agreements and Compliance webpage.
-
The IDS partial login experience is being updated. When the tenant is not already provided by the application, users will be asked to enter their IDS Tenant Name directly instead of entering an email address and selecting an organization area from a list.
- Previous partial login sign-in journey: The previous flow used two screens. Users first entered an email address. IDS then displayed a searchable list from which the user selected an organization area.
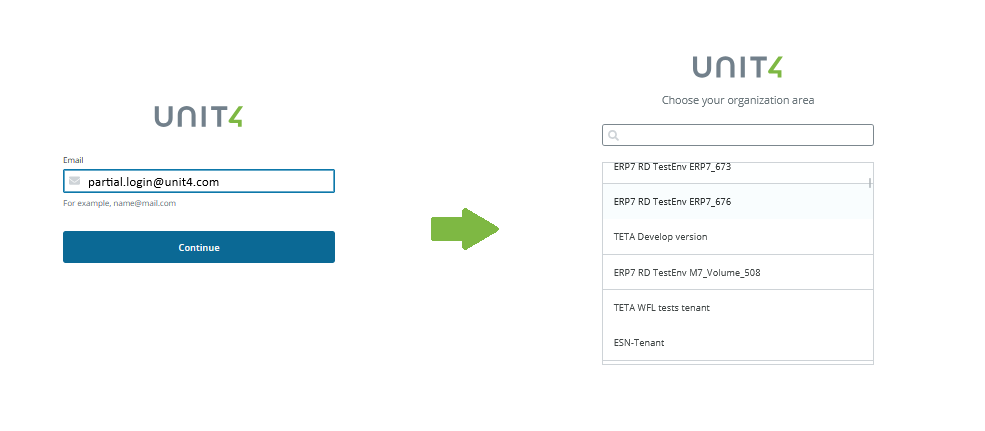
Figure 1. The previous patial login flow. - New partial login sign-in journey: The new flow replaces both discovery screens with a single tenant-entry screen. Users enter the IDS Tenant Name directly and select Continue.
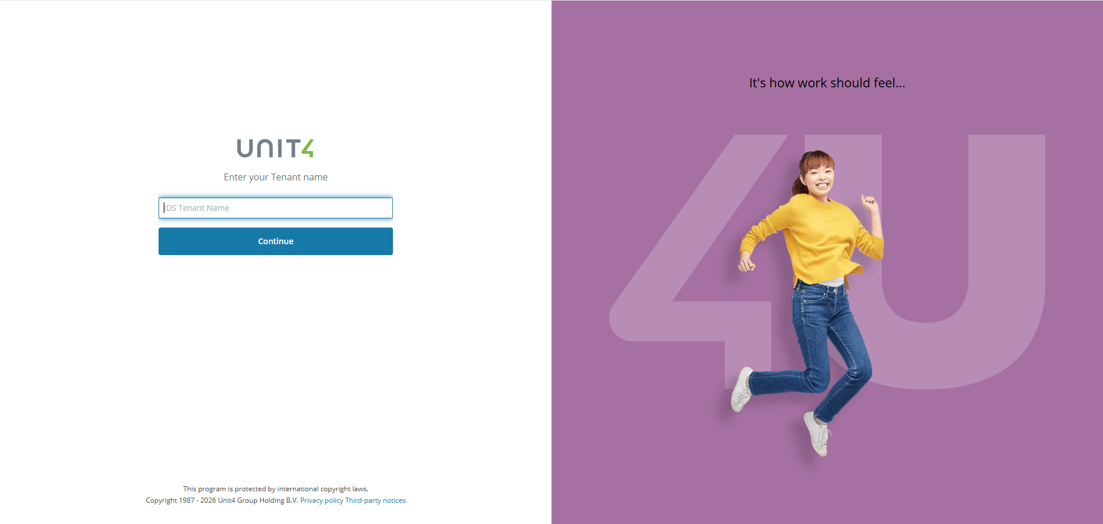
Figure 2. The new patial login flow.
June 2026
-
Support for PKCE with external IDP authentication through a new tenant setting.
- PKCE will be selected by default for every new OpenID Connect identity provider configuration added to an IDS tenant. This provides additional protection during the authorization code exchange while keeping the configuration process straightforward.
- Existing identity provider configurations will not be changed automatically and will continue to use their current authentication configuration. Customers wishing to enable PKCE for an existing configuration should submit a request to Unit4 so that the change can be coordinated and applied to the relevant tenant.
-
Consent screen: consent decisions for offline access scope are now remembered. The consent screen is not shown each time this scope is requested.
April 2026
Consent screen: opt-in model and remembering disallowed scopes
- Opt-in model: only required scopes are pre-selected. Users must explicitly select optional scopes they want to allow.
- Remembering disallowed scopes: both allowed and disallowed scopes are now stored. The consent screen is no longer shown for previously disallowed scopes.
- Note: if offline access scope was requested, the consent screen will always be displayed.
- Consent reset: due to database changes, all existing consents will be reset. Users will be prompted to provide consent again on first login after the update.
July 2025
Asymmetric Key Client authentication
Support for client authentication method based on asymmetric keys. Instead of transmitting a shared secret, the client authenticates by signing a JWT with its private key, which is validated using the corresponding public key stored in U4IDS. For implementation details check Tutorials/Setup Private Key JWTs for more information.